CyberTwin
(01)THE DELIVERABLE

The report, before the signup.

The exact deliverable, rendered as it ships — built on a fictional demo tenant, Acme Capital, so we can publish every page in the open. Every number is labeled proven from config, or modeled and shown as such.

NO SIGNUPNO CARDNO AGENTFICTIONAL COMPANY, REAL ENGINE RUN
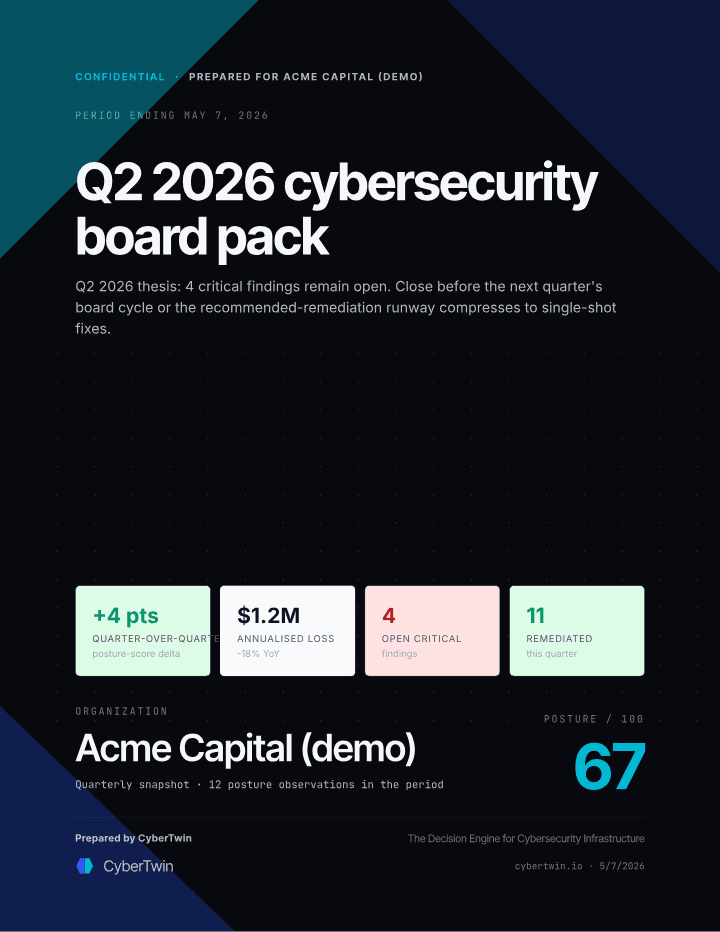
FIG.01 // BOARD PACKSAMPLE
Sample CyberTwin board pack — page-1 cover
Quarterly board pack · page 1 · sample
(02)HONEST GRADE

Same rubric, both stacks.

When CyberTwin recommends a stack, it runs that stack through the same rubric it used to grade your current setup — and shows you the number. The recommended Balanced stack scores 64/100; the Advanced upgrade scores 72/100. You decide whether the delta is worth it.

FIG.02 // GRADE · ONE RUBRICFICTIONAL COMPANY · MODELED
BALANCED
the recommended stack
64/100
ADVANCED
the upgrade · up to +$82K/yr list price
72/100
covers code-to-cloud appsec; 5 PCI DSS must-haves stay open
// THE FULL RUBRIC, CARD BY CARD ↓
The full rubric, card by card.

Where the 8 points come from.

Strengths, gaps and trade-offs for each stack — scored by the same rubric that grades the setup you run today. You decide whether the upgrade is worth it.

Sample fintech · Balanced stack
64/ 100
$203,635/yr · the recommended stack · 1 pick not priced (Nightfall AI), excluded from the total
Strengths
  • ✓Identity: Microsoft Entra ID P2
  • ✓Managed EDR: Huntress Managed EDR
  • ✓SIEM: Microsoft Sentinel
  • ✓Privileged access: Delinea Secret Server Cloud
Gaps
  • ·6 must-have capabilities unmet: code-to-cloud appsec and 5 cardholder-data (PCI DSS) controls
  • ·Nightfall AI has no sourced price, so fitting the budget is unconfirmed
Sample fintech · Advanced stack
72/ 100
$285,979/yr · up to +$82K/yr in list price over Balanced
Strengths
  • ✓Managed detection: CrowdStrike Falcon Complete
  • ✓Cloud security: Wiz Cloud Security Platform
  • ✓Application security: Veracode Application Security Platform
  • ✓Identity: Microsoft Entra Suite
  • ✓Covers code-to-cloud appsec, the must-have Balanced leaves open
Trade-offs
  • ·5 cardholder-data (PCI DSS) must-haves still unmet
  • ·Over the sample's budget ceiling by $35,979/yr

Engine output, not marketing math: both scores follow one rubric, published at /methodology, from the same engine run as the fintech sample PDF on this page, at catalog list prices. Totals sum priced picks only. The New Architecture view below draws the stack builder's own fintech profile, a slightly different seed, so its totals can differ.

(03)THREE REPORTS, ONE ENGINE

Each assessment ships its own report.

New Architecture, Architecture Review, and Configuration Review each generate a different deliverable. Below is a sample of each for the fictional Acme Capital — real engine-output shape, with the architecture diagram (SVG / PNG export) and the rules sheet.

generated 2026-05-07 · sample · fictional Acme Capital · 200-person fintech · illustrative sample, same layout as your own uploads

Three priced stacks

Engine output for the 200-person fintech / payments sample profile — the same run behind the fintech sample PDF. List prices dated 2026-09-25 · modeled, not a quote.

Lean
$79,843/yr · list
Posture 28/100 (engine grade) · 7 products · 18 weeks to stand up

No 24x7 managed detection in this stack — after-hours incident response relies on your own team (declared on-call: business hours).

  • ✓Microsoft Entra ID P1$16,800
  • ✓AWS GuardDuty + Security Hub$4,800
  • ✓Microsoft Sentinel$15,695
  • ✓Veeam Data Platform Foundation$4,650
  • ✓Amazon Inspector + AWS Config$6,000
  • +2 more in the PDF
BalancedRecommended
$216,335/yr · list · +1 not priced
Posture 64/100 (engine grade) · 14 products · 33 weeks to stand up

1 pick is not priced (Nightfall AI) — the $216,335 total excludes it, so fitting the $250,000 budget ceiling is unconfirmed; each pick says why.

  • ✓Veeam Data Platform Foundation$4,650
  • ✓Microsoft Sentinel$15,695
  • ✓Microsoft Entra ID P2$24,000
  • ✓Huntress Managed EDR$23,970
  • ✓AWS GuardDuty + Security Hub$4,800
  • +9 more in the PDF
Advanced
$291,479/yr · list
Posture 72/100 (engine grade) · 13 products · 43 weeks to stand up

Exceeds the stated $250,000 budget ceiling by $41,479/year.

  • ✓Veracode Application Security Platform$23,774
  • ✓Cloudflare WAF$2,400
  • ✓Business$22,000
  • ✓Microsoft Entra Suite$28,800
  • ✓Microsoft Sentinel$15,695
  • +8 more in the PDF

Not a fintech, not 200 people? Build the three stacks for a company like yours →

Recommended configuration to deploy

The architecture, ready to hand to an engineer or auditor.

Sample · Acme Capital reference architecture
EMAILIDENTITYENDPOINTNETWORKCLOUDSIEMDATADefender for O365MimecastEntra ID · SSO + CAOktaDefender for EndpointCrowdStrike FalconFortiGate · FW + SSL-VPNCloudflare WAFAWS IAM + ConfigAzure RBACMicrosoft SentinelSplunkS3 · customer PIIRDS · payments DBSecrets Mgr · Stripe keys

Tools grouped by architecture layer; edges show the protection and data-flow relationships the engine maps. Red-bordered nodes are the crown-jewel data stores. Export as SVG or PNG to hand to an auditor.

Compliance to implement

3 frameworks the sample fintech engine run targets · Balanced stack · MODELED
  • SOC 211 of 11 controls assessedEXPLICIT91/100
  • PCI DSS v47 of 8 controls assessedEXPLICIT84/100
  • ISO 270018 of 93 controls assessedEXPLICIT84/100

Roadmap

The sample FortiGate config's findings, sequenced by severity — Now / Next / Later.

Now
  • · Admin accounts without two-factor authentication
  • · Admin accounts without a password
  • · SSH version 1 enabled
  • · WAN interfaces allow HTTPS management
  • +2 more in the rules sheet
Next
  • · Admin accounts accept logins from anywhere
  • · IPsec tunnels use weak DH groups
  • · IPsec tunnels negotiate over IKEv1
  • · Strong cryptography (`strong-crypto`) is disabled
  • +7 more in the rules sheet
Later
  • · Default `admin` account present
  • · Admin idle timeout too long
  • · Two admin accounts use the super_admin profile
  • · Firewall running standalone (no HA)
  • +15 more in the rules sheet
(04)PERSONALIZE

See a sample built for your industry.

The default sample is a fictional fintech. If you're in healthtech, SaaS, e-commerce, or another sector, generate a personalized version showing the vendors, frameworks, and compliance scoring that match your environment.

One fictional company per industry, with its own region and frameworks. Marked “Sample report”.
(05)THE DELIVERABLES

12 boardroom-grade reports. One upload.

Every report is built from the same uploaded data. Each preview below is a real, downloadable PDF — rendered from the seeded Acme Capital environment, not a comp.

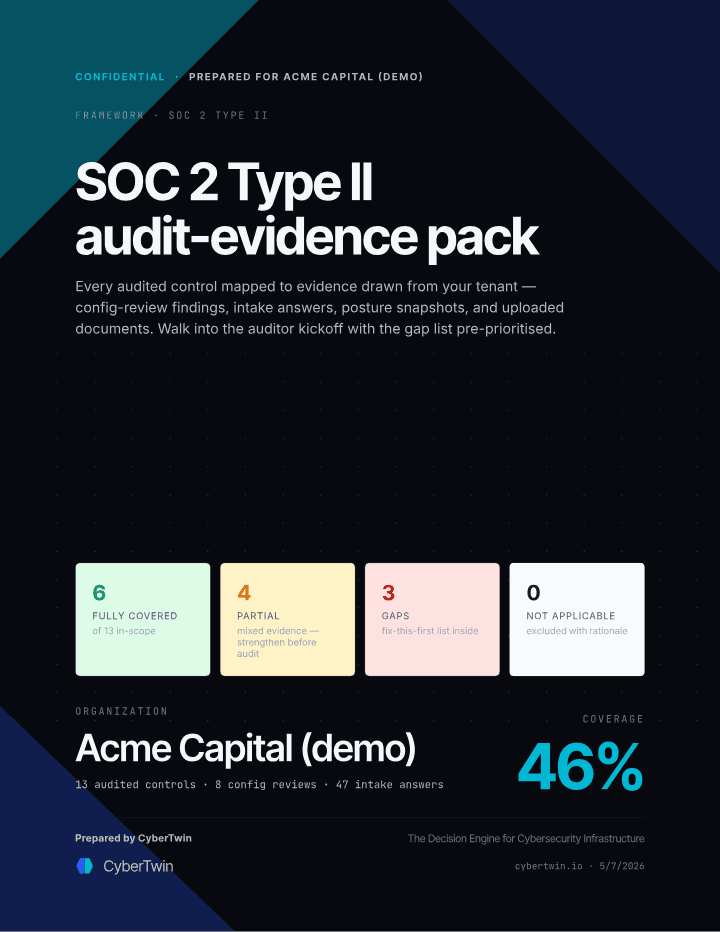
Audit-evidence pack — sample PDF cover

Audit-evidence pack

Every audited control in SOC 2, ISO 27001, PCI DSS v4, and NCA ECC v2 mapped to specific evidence — config-review findings, intake answers, posture snapshots, uploaded documents. Effort-ranked gaps with remediation guidance.

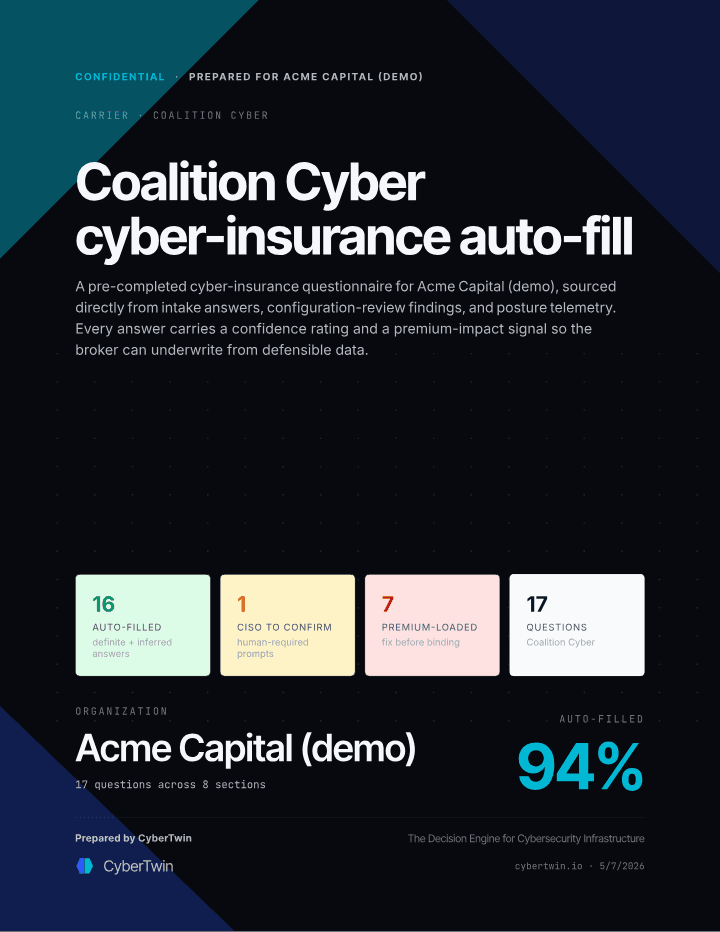
Cyber-insurance auto-fill — sample PDF cover

Cyber-insurance auto-fill

Pre-filled questionnaires for the major cyber insurance carriers. Each answer carries a confidence tag (definite / inferred / human-required) and a premium-impact signal (helpful / neutral / loaded). Premium-loaded answers ranked first.

Quarterly board pack — sample PDF cover

Quarterly board pack

Posture trend (12-month sparkline), ALE year-over-year as a modeled range, top open and remediated critical findings, and framework coverage counted by the evidence behind each control.

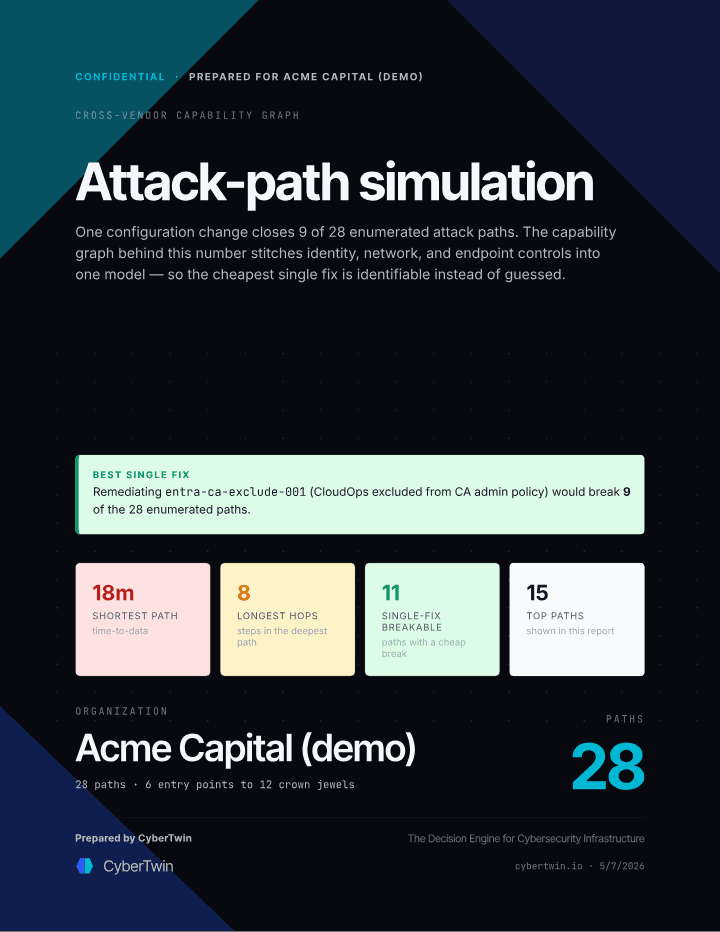
Cross-vendor attack-path simulation — sample PDF cover

Cross-vendor attack-path simulation

Attack-path mapping across the security tools you actually run. Uploads from 14 of them feed the graph today: Microsoft Entra, Okta, JumpCloud, AWS IAM (identity) · FortiGate, PAN-OS, Cisco ASA, Cisco Meraki (network) · Cloudflare (web application firewall) · Microsoft Defender for Endpoint, CrowdStrike Falcon (endpoint) · AWS Config (cloud) · Microsoft Defender for O365 (email) · Microsoft Sentinel (SIEM). BFS from each entry to each sensitive resource. Edges annotated with MITRE technique codes (26 distinct techniques). Paths matched against 11 threat-actor categories. Diagram uploads are read for follow-up questions only — they are not yet turned into topology, and reading diagram images (PNG / JPG) is paused.

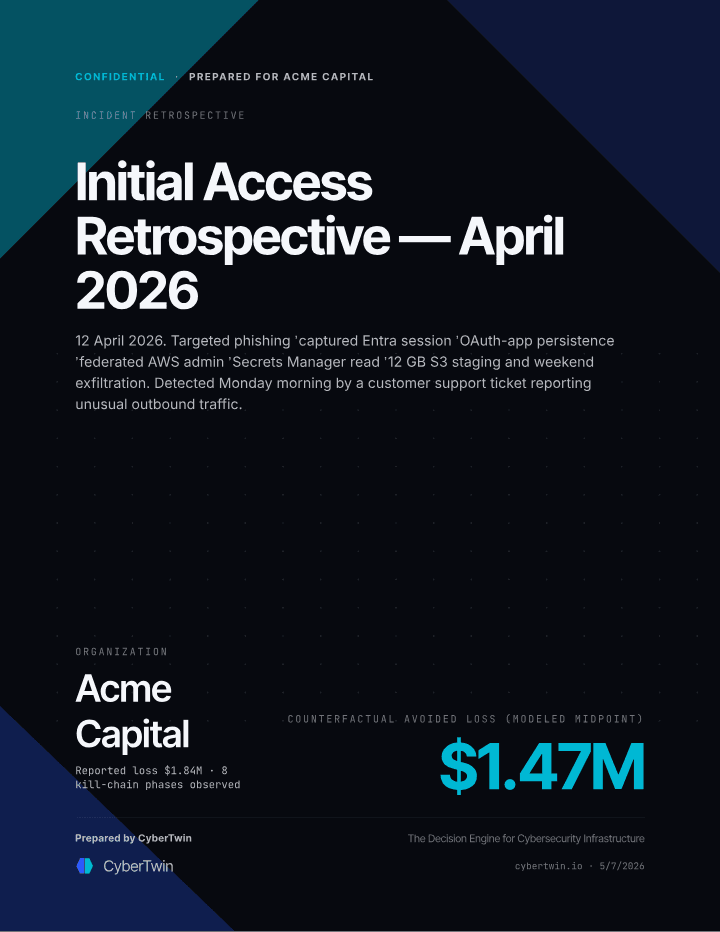
Incident retrospective — sample PDF cover

Incident retrospective

Walks an incident through the MITRE kill-chain. Shows which open findings would have broken the chain at each phase. Counterfactual loss avoided. Used post-incident or for tabletop preparation.

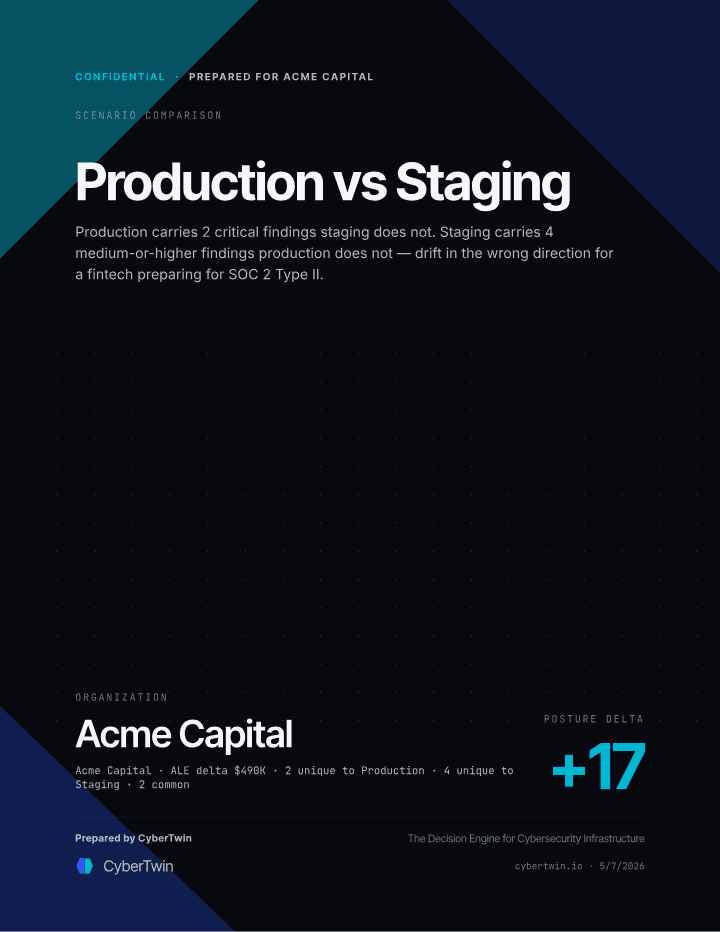
Multi-environment diff — sample PDF cover

Multi-environment diff

Compare prod vs staging, region A vs B. Diffs findings, severity counts, framework coverage, intake answers, ALE. The report that catches drift before audit.

Personalized Deployment Plan

Length depends on your stack · GENERATED IN-APP

Every product in the Balanced stack — only those — in deployment order. Architecture diagram annotated with deployment-order numbers and integration arrows color-coded by fit class. A written setup guide per product where one exists, with template variables substituted to your environment (org name, primary IdP, primary cloud, network seed subnet); each guide is a draft your team reviews before production. Inline integration handoffs between consecutive products. On Operate and above, per-step compliance annotation pins each setup step to specific framework controls (SOC 2 CC6.1, ISO 27001 A.5.17, NCA ECC 2-2-3, etc.) and a coverage scorecard at the end shows X of Y framework controls satisfied. Honest empty-state cards for products without a written guide (vendor-doc + Configuration Review check pointers).

Not a report for the board. It is the working document your engineers build from. Included in every subscription; the per-step control tags and the coverage scorecard start on Operate.

WHICH PLAN SHIPS WHICH REPORT
Board pack (risk-quantified)Every tier
Compliance-only reportEvery tier
Auditor evidence packOperate+
Insurance questionnaire auto-fillOperate+
Attack-path simulation reportOperate+
Incident retrospectiveOperate+
Executive briefOperate+
Security questionnaire auto-answerOperate+
Scenario comparisonOperate+
Environment diffProgram
Year-in-reviewProgram
SAMA CSF quarterlyProgram
(06)THE DIAGRAM, EXPORTABLE

A real architecture render.

Engine output for the same fictional Acme Capital — exportable as SVG or PNG.

Sample · Acme Capital reference architecture
EMAILIDENTITYENDPOINTNETWORKCLOUDSIEMDATADefender for O365MimecastEntra ID · SSO + CAOktaDefender for EndpointCrowdStrike FalconFortiGate · FW + SSL-VPNCloudflare WAFAWS IAM + ConfigAzure RBACMicrosoft SentinelSplunkS3 · customer PIIRDS · payments DBSecrets Mgr · Stripe keys

Tools grouped by architecture layer; edges show the protection and data-flow relationships the engine maps. Red-bordered nodes are the crown-jewel data stores. Export as SVG or PNG to hand to an auditor.

AFTER YOU'VE SEEN THE SAMPLE

Run it against your real environment.

Sample reports are static fictional data. Your assessment uses your real intake, your real configurations, your real frameworks — signup to first PDF in a single session.